Who Gets a Pass: How Status and Politics Quietly Corrupt Security Enforcement
Every organization publishes security policies. Acceptable use agreements, access control protocols, incident reporting procedures — the documentation is often thorough, professionally written, and prominently distributed. Leadership points to these materials as evidence of a mature security posture. Yet in practice, a separate and entirely unwritten rulebook frequently governs how those policies are actually applied. It is a rulebook shaped not by compliance frameworks but by organizational politics, and its influence on your security culture may be far more corrosive than any external threat.
The uncomfortable truth is this: in most workplaces, who commits a security violation matters as much as what violation was committed. Status, perceived influence, and proximity to leadership all function as invisible variables in the enforcement equation — and the results are rarely uniform.
The Unwritten Hierarchy of Accountability
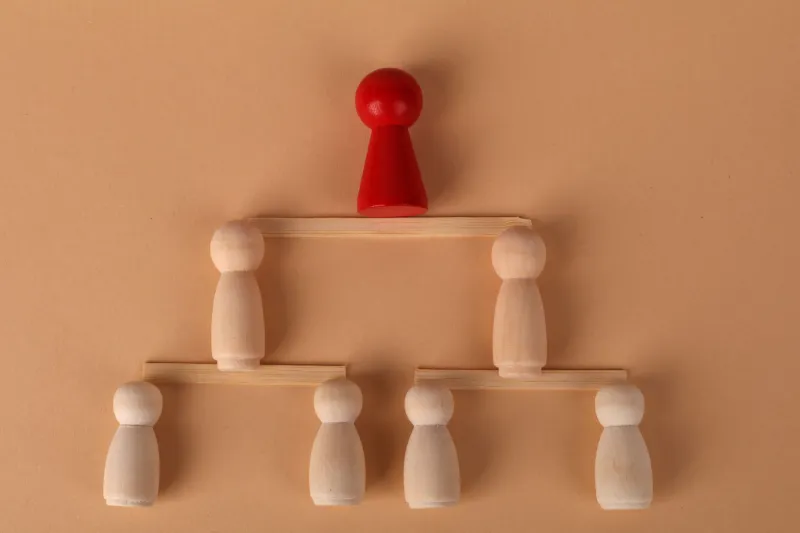
Organizational research has long documented that employees navigate two parallel structures simultaneously: the formal hierarchy printed on the org chart, and the informal power structure that actually governs day-to-day decisions. In healthy organizations, these two structures largely align. In many others, they diverge significantly — and nowhere is that divergence more dangerous than in the domain of security.
Consider a straightforward scenario. A junior analyst tailgates through a secured door without badging in. A colleague observes the incident and reports it. Now imagine the same act committed by a senior vice president. Studies on workplace reporting behavior consistently find that employees are significantly less likely to flag violations committed by individuals they perceive as powerful, influential, or socially connected. The calculus is not irrational — it reflects a learned understanding of organizational consequences. Reporting a peer is manageable. Reporting someone who controls your performance review, your project assignments, or your professional reputation is an entirely different proposition.
This asymmetry does not require malicious intent to take root. It emerges organically from the social dynamics that exist in virtually every workplace. But its effect on security is systemic and serious.
When Exceptions Become Expectations
The first time a senior leader bypasses the multi-factor authentication requirement because it is inconvenient, and nothing happens, a precedent is quietly established. The first time a high-revenue sales executive shares client data over an unsanctioned messaging platform and receives only a mild verbal reminder, the organization has effectively communicated that the rules are negotiable — provided you occupy the right position.
Over time, these individual exceptions accumulate into something larger: an implicit organizational norm that security requirements are enforced selectively based on status. Employees who observe this pattern do not typically respond by escalating their own compliance. Research on organizational fairness consistently demonstrates that perceived inequity in rule enforcement erodes broader adherence. When people believe the rules do not apply equally, their motivation to follow those rules — even when it is inconvenient — diminishes measurably.
The result is a security culture with a hidden stratification problem. On paper, everyone is subject to the same policies. In practice, a tiered system of accountability operates beneath the surface, and the individuals most likely to be granted informal exemptions are often those with the broadest system access and the greatest potential to cause harm if compromised.
The Reporting Chilling Effect
The asymmetry in enforcement is compounded by a parallel asymmetry in reporting. Security incident reporting systems are premised on the assumption that employees will come forward when they observe something concerning. That assumption holds reasonably well when the subject of the report is a peer or a lower-status colleague. It breaks down considerably when the offender is someone with organizational authority.
Employees who consider reporting a senior colleague's security lapse face a complex set of social and professional risks. Will the report be taken seriously, or quietly dismissed? Will the act of reporting itself generate retaliation — formal or informal? Is there a realistic expectation that anything will change, or will the incident be absorbed without consequence? In organizations where political dynamics are strong and reporting culture is weak, the rational response for many employees is silence.
This chilling effect is particularly acute in sectors where hierarchical culture is pronounced — financial services, defense contracting, healthcare administration — but it is by no means limited to those industries. Any organization in which leaders visibly receive different treatment than their subordinates is cultivating the conditions for underreporting.
Security Leadership's Difficult Position
Chief information security officers and their teams are rarely blind to these dynamics. Many security professionals are acutely aware that certain individuals in their organizations are effectively beyond the reach of standard enforcement mechanisms. The challenge is that directly confronting this reality requires a level of organizational authority and executive backing that security leaders frequently lack.
When a CISO escalates a concern about a C-suite executive's security behavior, the outcome depends almost entirely on how much genuine support that CISO has from the board and senior leadership. In organizations where security is treated as a cost center rather than a strategic function, that support is often insufficient. The result is that security leaders learn to work around the political landscape rather than through it — a pragmatic adaptation that nonetheless reinforces the very hierarchy they are trying to neutralize.
Structural Remedies Worth Considering
Addressing the intersection of organizational politics and security enforcement requires interventions that operate at the structural level, not merely the policy level. Several approaches have demonstrated meaningful impact in organizations committed to genuine reform.
Anonymous reporting mechanisms with genuine independence. Reporting channels that route through HR or direct management are inherently vulnerable to political interference. Third-party reporting platforms, with verifiable anonymity protections and independent review processes, reduce the social calculus that discourages reporting of high-status offenders.
Visible, documented enforcement at all levels. When leadership visibly subjects itself to the same security requirements as the broader workforce — and when exceptions are formally documented and justified rather than informally granted — the implicit hierarchy of accountability begins to flatten. This requires deliberate demonstration, not passive expectation.
Security metrics that track reporting equity. Organizations that measure not only incident volume but the distribution of reported incidents across organizational levels are better positioned to identify enforcement gaps. A reporting pattern in which violations are overwhelmingly attributed to junior employees warrants careful examination.
Board-level accountability for security culture. When boards receive regular reporting on security culture indicators — including enforcement consistency — the organizational pressure to maintain genuine uniformity increases. Security culture cannot be delegated entirely to the CISO if it is to function effectively at the leadership tier.
A Culture Defined by Its Edges
Organizational culture is ultimately defined not by its written policies but by the behaviors it tolerates at its margins. A security culture that enforces rules rigorously for some employees while quietly accommodating the preferences of others is not a security culture in any meaningful sense. It is a performance of security — one that may satisfy auditors while leaving the organization's actual risk exposure largely unaddressed.
The informal hierarchies that shape your workplace are not going away. They are a feature of human social organization, present in every industry and at every organizational scale. What security leaders and executives can control is whether those hierarchies are permitted to silently govern security enforcement — or whether the organization builds the structural safeguards necessary to ensure that the rules apply, consistently and visibly, to everyone who walks through the door.
The answer to that question will tell you more about your true security posture than any policy document ever could.