The Open Door Policy You Never Meant to Create: Insider Threats and the Collaboration Tool Problem
There is a particular irony embedded in the modern American workplace. Organizations invest heavily in endpoint protection, network monitoring, and perimeter security—then watch their employees conduct sensitive business conversations in channels that receive roughly the same security scrutiny as a break room bulletin board.
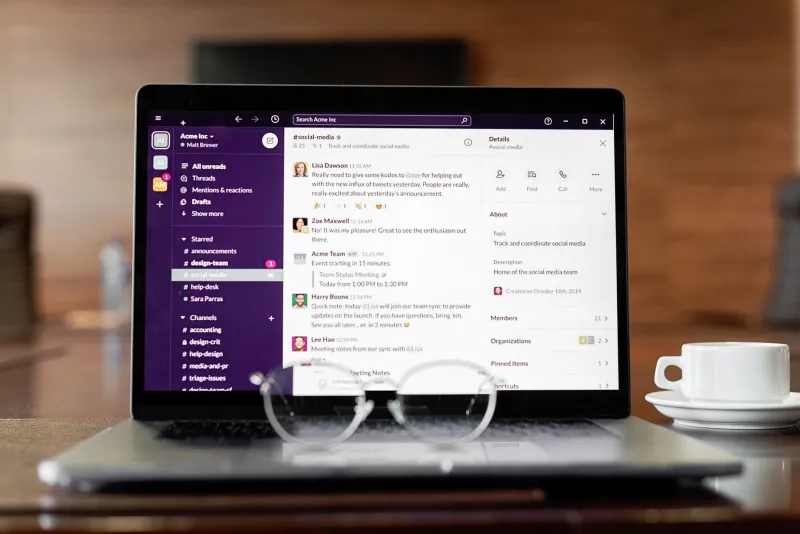
Collaboration platforms have become the connective tissue of organizational life. Slack alone reports more than 32 million daily active users. Microsoft Teams surpassed 300 million monthly active users in 2023. These are not peripheral tools. They are, for many organizations, the primary venue through which decisions are made, files are shared, relationships are built, and institutional knowledge is transferred. And yet, a persistent gap exists between how these platforms are used and how seriously they are secured.
That gap is precisely where insider threats—and the social engineers who cultivate them—tend to operate.
Why Collaboration Platforms Are Uniquely Vulnerable
The design philosophy behind tools like Slack and Teams is fundamentally oriented toward reducing friction. Channels are easy to create. File sharing is seamless. Integrations with third-party applications are encouraged. Direct messaging is instantaneous and informal. These qualities make the platforms extraordinarily useful. They also make them structurally difficult to monitor and control.
Unlike email—which most organizations subject to archiving, filtering, and policy enforcement—collaboration tool communications often exist in a regulatory gray zone. Many organizations have robust email security postures and virtually no equivalent governance for their messaging platforms. Employees frequently treat these channels as ephemeral, conversational spaces rather than official records, which means they exercise less judgment about what they share.
The informal tone of these environments compounds the problem. When a colleague messages you on Slack asking for a quick favor, the social context feels fundamentally different from a formal email request. That informality is not accidental—it is engineered into the product. But it also lowers cognitive defenses in ways that threat actors have learned to exploit systematically.
The Insider Threat Landscape Within Messaging Tools
Insider threats take several forms, and collaboration platforms serve each of them differently.
For the malicious insider—an employee who has made a deliberate decision to harm the organization—these tools offer a low-friction exfiltration pathway. Sensitive documents, client data, proprietary code, and internal strategy discussions can be accessed and forwarded with minimal technical sophistication. Unlike network-level data exfiltration, which may trigger security alerts, moving a file from a shared Slack channel to a personal device often generates no automated response whatsoever.
For the negligent insider—an employee who causes harm through carelessness rather than intent—collaboration platforms amplify the risk of accidental exposure. Oversharing in a channel with broader membership than the employee realizes, connecting an unvetted third-party app through a platform integration, or responding to a message without verifying the sender's identity are all common failure modes that these environments actively enable.
Perhaps most underappreciated is the role these platforms play in enabling the compromised insider—an employee who has become, wittingly or not, an instrument of an external threat actor. Social engineering campaigns increasingly use collaboration tools as their primary attack surface, precisely because they offer direct access to employees in an environment where skepticism is low and verification habits are weak.
How External Actors Move Through Internal Channels
The pathway from external attacker to trusted internal presence is shorter than most security leaders acknowledge.
In organizations that use Slack Connect—a feature that allows external parties to join shared channels—or that integrate third-party contractors into their Teams environment, the boundary between inside and outside becomes genuinely blurry. A threat actor who compromises a vendor's account, or who creates a convincing impersonation of one, can gain access to internal conversations without ever breaching the organization's primary network.
Once inside, the attacker's strategy typically mirrors the playbook of long-game social engineering: building rapport gradually, establishing credibility through small helpful interactions, and identifying the individuals most likely to respond to requests for sensitive information or access. The informal nature of the platform works in the attacker's favor. Employees who would scrutinize an unusual email request may respond to the same request in a DM without a second thought.
Workspace enumeration—the process of mapping an organization's internal structure through publicly visible channel names, user directories, and pinned messages—can also yield significant intelligence for attackers who gain even limited access. Channel names alone often reveal organizational priorities, active projects, and the identities of key personnel.
The Governance Gap Organizations Need to Close
Addressing this threat surface requires a shift in how organizations categorize and govern their collaboration tools. Treating these platforms as communication utilities rather than security perimeters is a posture that no longer reflects the risk environment.
Several practical measures can meaningfully reduce exposure without undermining the productivity value these tools provide.
Access governance deserves the same rigor applied to other systems. User provisioning and deprovisioning for collaboration platforms should be integrated into standard identity lifecycle management. Former employees with active Slack or Teams accounts represent a persistent and entirely preventable risk.
Third-party integrations should be subject to formal review. The app ecosystems built around major collaboration platforms are vast, and many integrations request broad data permissions. Organizations should maintain an approved integration list and enforce it through administrative controls rather than relying on employee discretion.
External access policies need explicit definition. If contractors, partners, or clients are granted access to internal channels, those arrangements should be governed by documented policies that specify what information can be shared in those spaces and what cannot.
Message retention and audit logging should be enabled and reviewed. Many organizations have the technical capacity to retain and audit collaboration platform communications but have not implemented the relevant policies. In the context of an insider threat investigation, this data can be invaluable. Its absence can be catastrophic.
Employee awareness training must explicitly address these platforms. Security awareness programs that focus on email phishing while ignoring collaboration tool threats are training employees for the last war. Scenarios involving impersonation through DMs, suspicious file share requests, and unusual integration prompts should be part of standard security education curricula.
Rethinking the Perimeter
The traditional concept of a security perimeter—defined by network boundaries and enforced through technical controls—has been eroding for years. Remote work, cloud adoption, and the proliferation of SaaS tools have each contributed to that erosion. Collaboration platforms represent one of the most significant and least addressed dimensions of this shift.
The organizations best positioned to manage this risk are those that approach human behavior as a security variable with the same seriousness they apply to technical configurations. The channels where your employees communicate informally are also the channels where trust is built, information is exchanged, and decisions are influenced. For anyone seeking to exploit your organization from the inside—or to work their way toward the inside—that combination is extraordinarily attractive.
Securing these environments is not primarily a technology problem. It is an organizational culture problem, a policy problem, and a human awareness problem. The tools to address it exist. The question is whether leadership is prepared to treat the collaboration platform as the security perimeter it has quietly become.